Somehow or other I can seem to get things working with Jamulus, but I really am struggling to explain how.
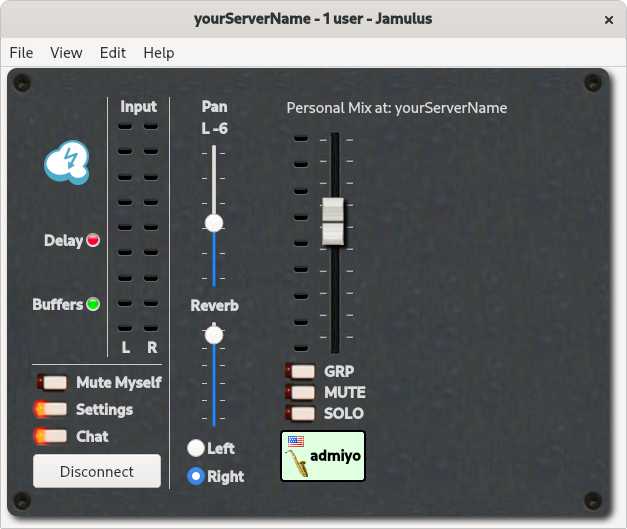
Somehow or other I can seem to get things working with Jamulus, but I really am struggling to explain how.
When I tried running SweetHome3D, I got two different problems depending on which of the scripts I tried. I eventually was able to get ./SweetHome3D-Java3D-1_5_2 to run. At first I got this error:
$ ./SweetHome3D-Java3D-1_5_2 Exception in thread "main" java.lang.UnsatisfiedLinkError: /home/ayoung/apps/sweet/SweetHome3D-6.4.2/lib/libj3dcore-ogl.so: libnsl.so.1: cannot open shared object file: No such file or directory |
I was able to resolve with guidance from this thread. I had to install libnsl .
$ yum search libnsl ========================= Name Exactly Matched: libnsl ========================= libnsl.i686 : Legacy support library for NIS libnsl.x86_64 : Legacy support library for NIS ======================== Name & Summary Matched: libnsl ======================== libnsl2-devel.i686 : Development files for libnsl libnsl2-devel.x86_64 : Development files for libnsl ============================= Name Matched: libnsl ============================= libnsl2.x86_64 : Public client interface library for NIS(YP) and NIS+ libnsl2.i686 : Public client interface library for NIS(YP) and NIS+ [ayoung@ayoungP40 SweetHome3D-6.4.2]$ sudo yum install libnsl |
And then it runs.
While reviewing the comments on the Ironic spec, for Secure RBAC. I had to ask myself if the “project” construct makes sense for Ironic. I still think it does, but I’ll write this down to see if I can clarify it for me, and maybe for you, too.
Continue readingOpenShift requires a load balancer for providing access to the hosted applications. Although I can run a three node cluster, I need a fourth location to provide a load balancer that can then provide access to the cluster.
For my home lab set up, this means I want to run one on my bastion host….but it is already running HTTP and (FreeIPA) Red Hat IdM. I don’t want to break that. So, I want to add a second IP address to the bastion host, and have all of the existing services make use of the existing IP address. Only the new HA Proxy instance will use the new IP address.
This would be trivial for a simple Ethernet port, but I am using a Bridge, which makes it a touch trickier, but not terribly so.
Continue readingMy folks asked me to get my stuff out of their storage. Included was my old West Point uniforms…and something special.
Continue readingIn an OpenStack system, the communication between the compute nodes and the scheduler goes through a messaging system such as RabbitMQ. While there have been different models over the years, the basic assumption has remained that all actors identify themselves to the broker via a password and are trusted from that point forward.
What would happen if a compute node was compromised? The service running on the node could send any message one the bus that it wanted. Some of these messages are not ones that a compute node should ever send, such as “Migrate VM X to Node Y.” If the compromise was delivered via a VM, that hostile VM could then attempt to migrate itself to other nodes and compromise them, or could attempt to migrate other VMs to the compromised nodes and read their contents.
How could we mitigate attacks of this nature?
Continue readingIt’s been a while since I built my standing desk. Here’s the current state of it.
Continue reading